Australians reported 481,523 scams in 2025, with 274,577 reports involving financial losses totalling $2.18 billion.
Behind those numbers are scams that are becoming increasingly difficult to spot. For organisations, one of the most convincing can begin with something as routine as an invoice.
Invoice fraud is becoming increasingly sophisticated. The email may come from a supplier you know. The invoice may look exactly like previous ones. The amount is correct, the project is familiar, and the message may even sit inside a genuine email thread.
The only thing that's changed is the bank account.
That one change can redirect thousands of dollars into a cyber criminal's hands.
How it happens
Invoice fraud, also known as payment redirection fraud, is a common form of Business Email Compromise (BEC). Criminals gain access to a real email account - through phishing, stolen credentials, malware or a data breach - then quietly monitor it. They learn who approves payments, how invoicing cycles work, and wait for the right moment to intercept a genuine transaction and simply change the bank details.
Because nothing else changes, it's very hard to spot.
Example of What a Scam Looks Like
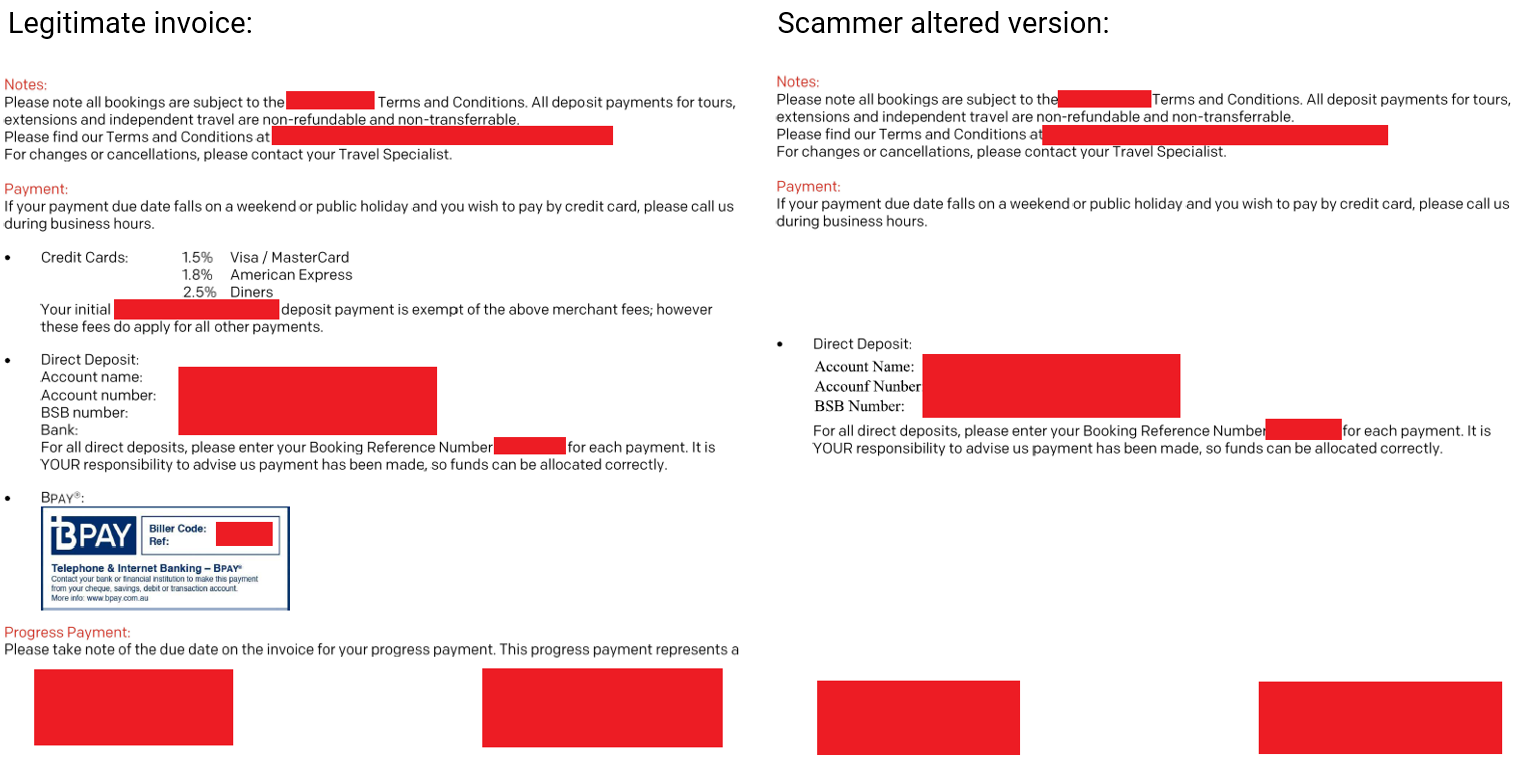
A Real Scenario
An organisation has worked with a trusted supplier for months. Invoices arrive regularly, and the next payment is due.
A member of the finance team receives an email from the supplier: their banking details have changed. An updated invoice is attached. The supplier's name is right. The invoice number is right. The amount is right. It's part of an existing conversation.
Nothing looks suspicious, but before processing the payment, the employee follows procedure and calls the supplier using the number already on file, not the one on the new invoice.
The supplier's bank details haven't changed. Their email account had been compromised, and a criminal was waiting for exactly this moment to redirect the payment.
One phone call prevented the loss. Without that simple check, a routine payment could have resulted in a substantial financial loss, with little to no chance, of recovering the funds.
The Golden Rule
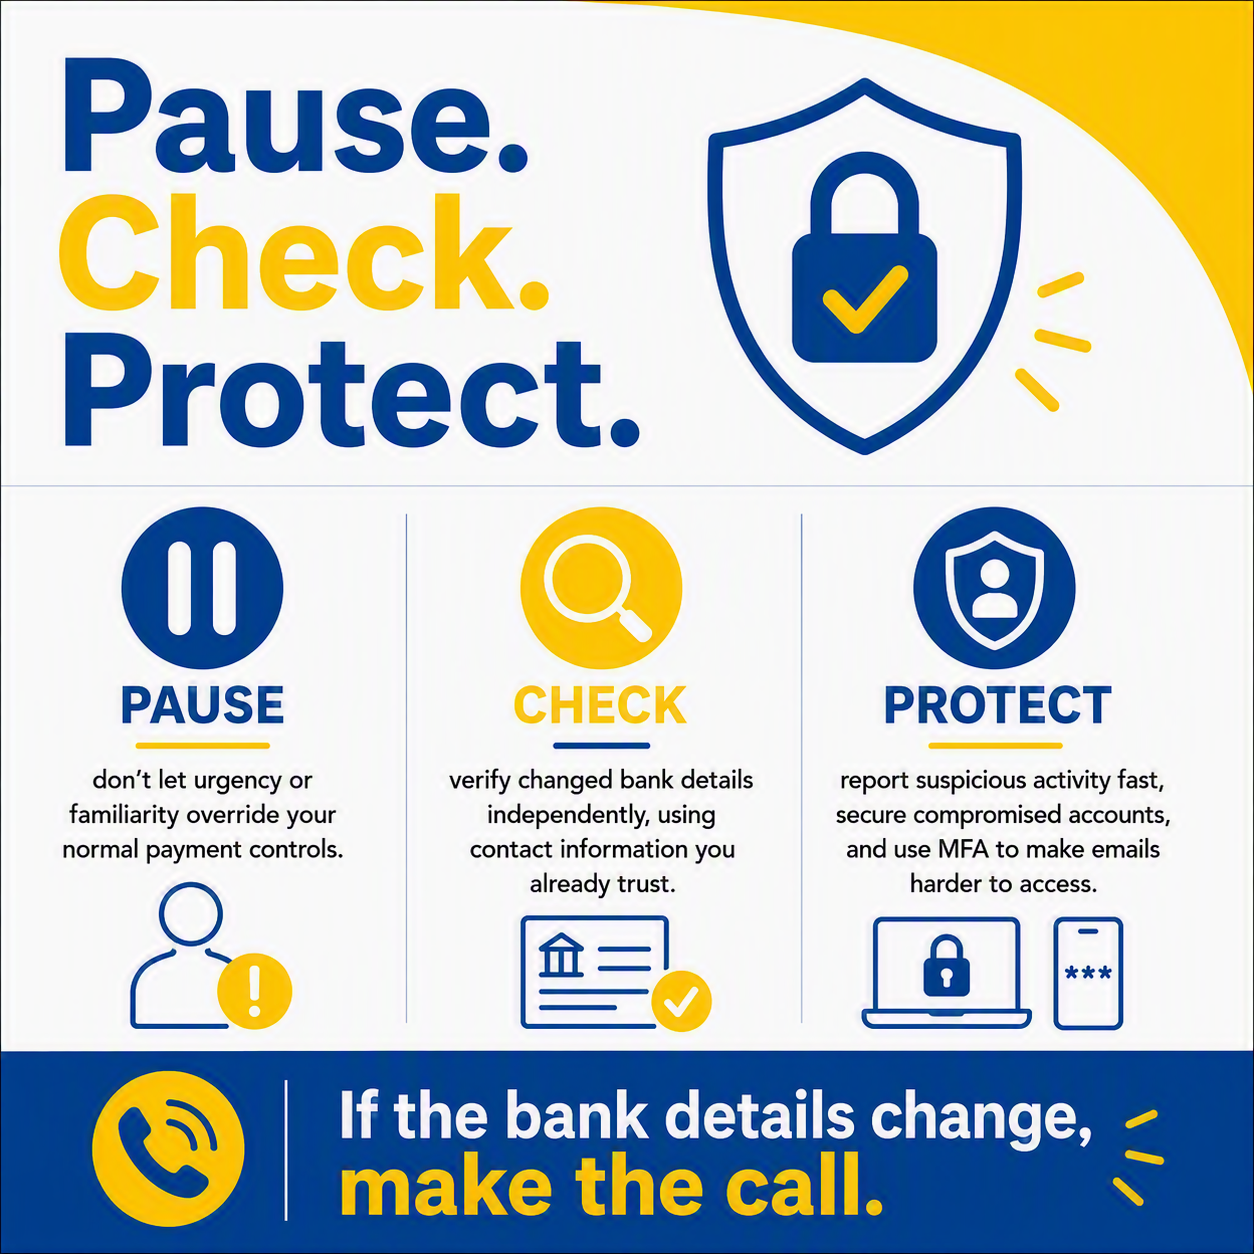
If bank details change, verify independently before you pay - using a phone number you already have on file, never the number on the new invoice or in the email.
Don't reply to the email to confirm the change either. If the account is compromised, you'd simply be asking the criminal to confirm their own fraud.
Build this into your Payment Process
Individual vigilance helps, but it shouldn't be the only line of defence. Consider:
- Independent verification of any request to change supplier or employee bank details, using contact details you already trust
- Separation of duties — the person changing supplier details shouldn't be the same person approving the payment
- Extra approval for large or unusual payments
- Clear procedures for urgent requests, including anything appearing to come from senior leadership
- MFA/2FA on email, financial systems and admin accounts, so a stolen password alone can't grant access
- Regular staff training on BEC and payment redirection scams
Don't Let Urgency Skip the Checks
Criminals rely on urgency to short-circuit good judgement — an overdue invoice, a supplier who "needs it today," a request that appears to come from the CEO. Treat pressure, secrecy, or a change in bank details as a reason to slow down, not speed up. Staff should always feel supported for pausing to verify, no matter who the request appears to come from.
If You've Already Paid
- Contact your bank immediately — speed matters
- Notify your IT/security team, in case an email account has been compromised
- Report it via ReportCyber and ScamWatch
Learn More About Staying Secure
We’re Here to Help
If you believe you’ve been a victim of a scam or are concerned about the security of your accounts, contact the CDF team today.
Share this article:
Related articles
CDPF Limited, a company established by the Australian Catholic Bishops Conference, has indemnified the Catholic Development Fund ABN 15 274 943 760 (the Fund) against any liability arising out of a claim by investors in the Fund. In practice, this means your investment is backed by the assets of the Catholic Archdiocese of Melbourne. The Fund is required by law to make the following disclosure. Investment in the Fund is only intended to attract investors whose primary purpose for making their investment is to support the charitable purposes of the Fund. Investors’ funds will be used to generate a return to the Fund that will be applied to further the charitable works of the Archdiocese of Melbourne and the Dioceses of Sale and Bunbury. The Fund is not prudentially supervised by the Australian Prudential Regulation Authority nor has it been examined or approved by the Australian Securities and Investments Commission (ASIC). An investor in the Fund will not receive the benefit of the financial claims scheme or the depositor protection provisions in the Banking Act 1959 (Cth). The investments that the Fund offers are not subject to the usual protections for investors under the Corporations Act (Cth) or regulation by ASIC. Investors may be unable to get some or all of their money back when the investor expects or at all and investments in the Fund are not comparable to investments with banks, finance companies or fund managers. The Fund’s identification statement may be viewed here or by contacting the Fund. The Fund does not hold an Australian Financial Services Licence.